Compliance platform comparison

Drata vs Secureframe

Secureframe's typical price is lower ($20,000 median against $25,000 median). Both publish 300+ integrations. Drata is listed by more audit firms in SOC2Auditors.org's directory (49 vs 13). On G2, Drata rates 4.7 from 1,397 reviews and Secureframe 4.7 from 835.

Short verdict: which one fits you

A fit guide, not a ranking. We don't pick an overall winner.

Choose Drata if…

  • you want more choice of audit firm (49 directory firms vs 13) [4]
  • you match its stated best fit: growth-stage SaaS teams that expect to add frameworks and want configurable tests [3]

Choose Secureframe if…

  • a lower typical price matters most ($20,000 median vs $25,000 median) [2]
  • you want guided preparation or included expert help [3]
  • you match its stated best fit: teams that want expert guidance on clearly named packages [3]

Neither runs the audit itself. If you want software and audit from one provider, compare Thoropass. [3]

Drata

Compliance automation platform with custom tests, compliance checks in infrastructure code and a dedicated auditor portal.

Typical annual price
$25,000 medianThird-party[2]
Observed contracts (Vendr)
$9,415 to $68,250Third-party[2]
G2 rating
4.7 · 1,397 reviewsUser reviews[1]
G2 time to implement
Integrations
Audit firms in the directory
49 directory firmsThird-party[4]
Default test cadence
Daily (7 pm PT)Vendor-reported[11]

Secureframe

Compliance platform sold as named packages (Fundamentals, Complete, Defense) with expert guidance.

Typical annual price
$20,000 medianThird-party[2]
Observed contracts (Vendr)
$7,733 to $32,575Third-party[2]
G2 rating
4.7 · 835 reviewsUser reviews[1]
G2 time to implement
Integrations
Frameworks
Not disclosedNot disclosed[3]
Audit firms in the directory
13 directory firmsThird-party[4]
Default test cadence
Daily to monthly, by testThird-party[13]

Pricing: is Drata or Secureframe cheaper?

Secureframe's typical price is lower ($20,000 median against $25,000 median).

Drata
$9,415 to $68,250Third-party[2]
Median $25,000
Secureframe
$7,733 to $32,575Third-party[2]
Median $20,000

Observed annual contract values reported by Vendr, read 5 October 2026. These are different buyers and scopes, not quotes. [2]

AttributeDrataSecureframe
Typical annual price
$25,000 medianThird-party[2]
$20,000 medianThird-party[2]
Observed contract range (Vendr)
$9,415 to $68,250Third-party[2]
$7,733 to $32,575Third-party[2]

Before comparing totals, get both quotes on the same written scope: employees, frameworks, modules, implementation, support level, contract term, renewal cap and the auditor's fee as its own line.

Integrations and automated testing

Both publish 300+ integrations.

AttributeDrataSecureframe
Integrations
Default test cadence
Daily (7 pm PT)Vendor-reported[11]
Daily to monthly, by testThird-party[13]

On G2, "Limited integrations" is among Drata's most-mentioned complaints (43 G2 mentions). [8]

On G2, "Integration issues" is among Secureframe's most-mentioned complaints (184 G2 mentions). [1]

Integration counts are vendor claims and are counted differently by each vendor. Test the systems you depend on during a trial.

Frameworks

Drata lists 30+; Secureframe doesn't publish a count.

AttributeDrataSecureframe
Frameworks published
Not disclosedNot disclosed[3]
ISO 27001
HIPAA

Capabilities compared

From SOC2Auditors.org capability profiles and vendor plan pages. "Not disclosed" means we could not confirm either way; it does not mean the feature is missing.

AttributeDrataSecureframe
Auditor workspace
Trust centre
SCIM provisioning
Add-on or higher tierVendor-reported[5]
Add-on or higher tierVendor-reported[12]
Audit from the same provider
Self-hosting option
Not disclosedNot disclosed[3]

Working with your auditor

Drata is listed by more audit firms in SOC2Auditors.org's directory (49 vs 13).

AttributeDrataSecureframe
Audit firms in the directory
49 directory firmsThird-party[4]
13 directory firmsThird-party[4]
Audit from the same provider

Drata doesn't sell the audit; you hire a firm separately. Secureframe doesn't sell the audit; you hire a firm separately. Directory counts are firms that list each platform, not partnerships or quality ratings. [4]

What reviewers say on G2

On G2, Drata rates 4.7 from 1,397 reviews and Secureframe 4.7 from 835.

Drata

Listing-site ratings
G2
4.7
1,397 reviews

Recurring praise

  • Customer support135 G2 mentions
  • Ease of use115 G2 mentions

Recurring complaints

  • Limited integrations43 G2 mentions

Secureframe

Listing-site ratings
G2
4.7
835 reviews

Recurring praise

  • Ease of use650 G2 mentions
  • Compliance552 G2 mentions

Recurring complaints

  • Integration issues184 G2 mentions
  • Limited customization141 G2 mentions

Source: [1][8]

G2 time to implement: Drata 2 months, Secureframe 2 months. Mention counts scale with review volume, so compare them as proportions, not totals. [1]

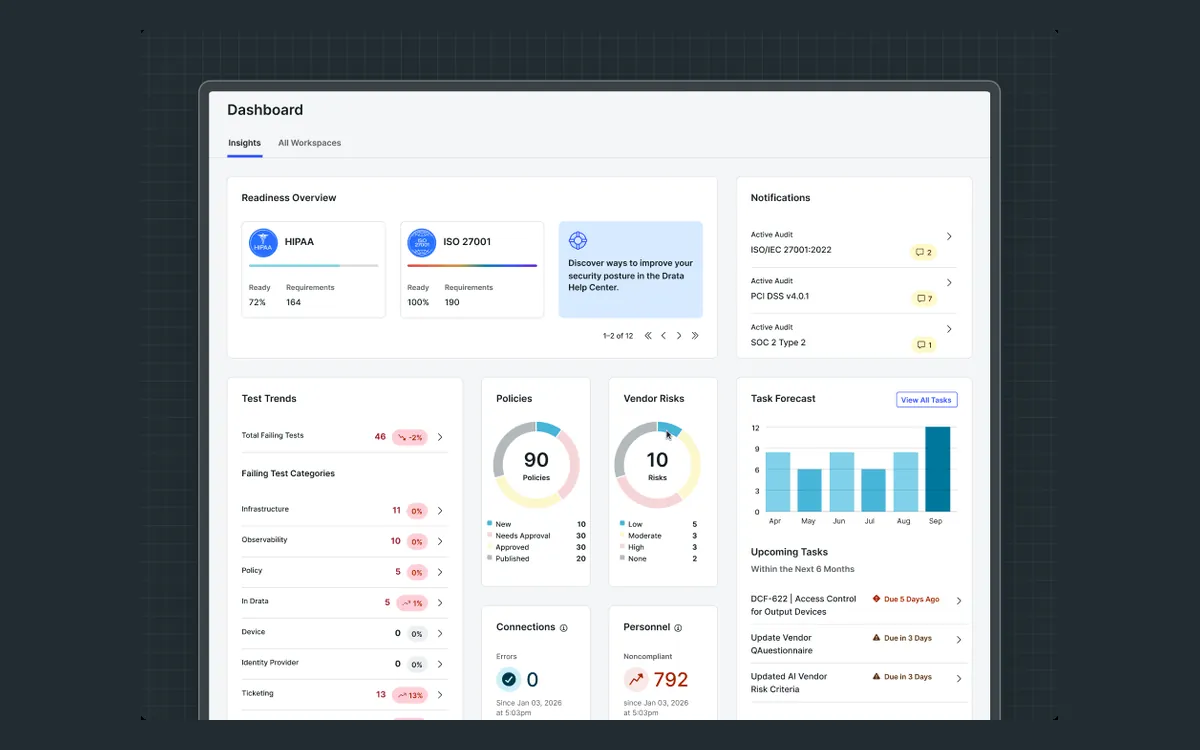
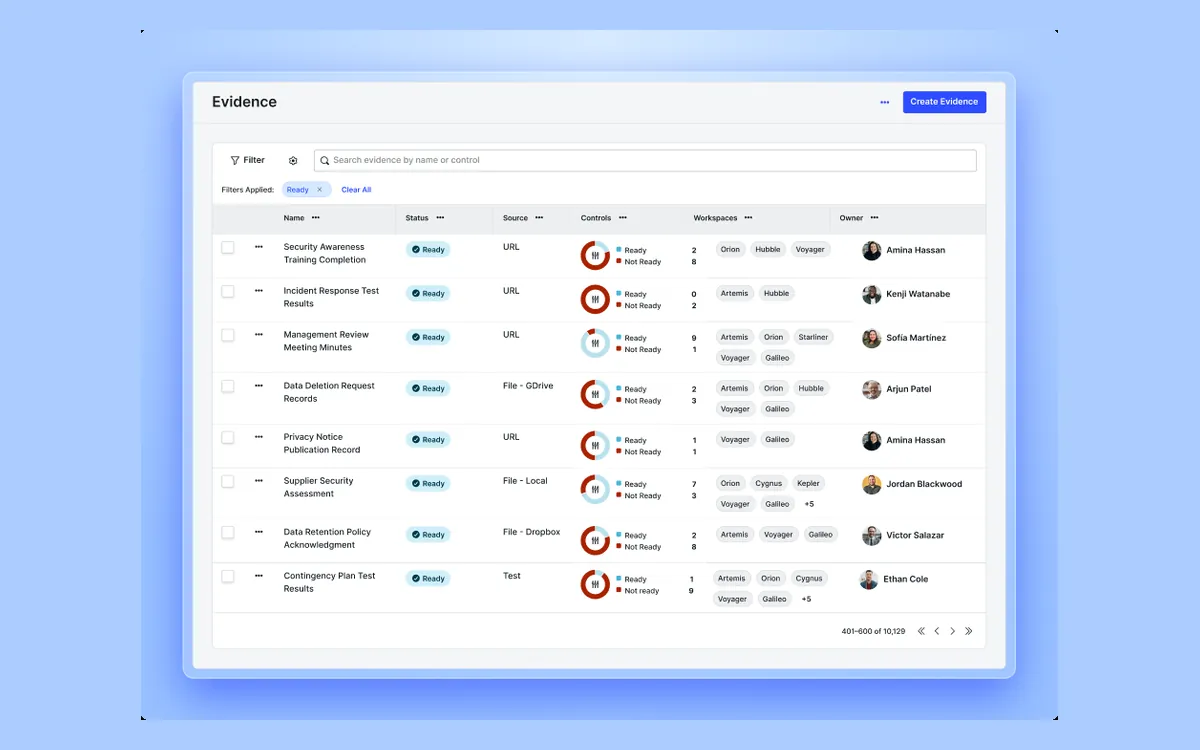
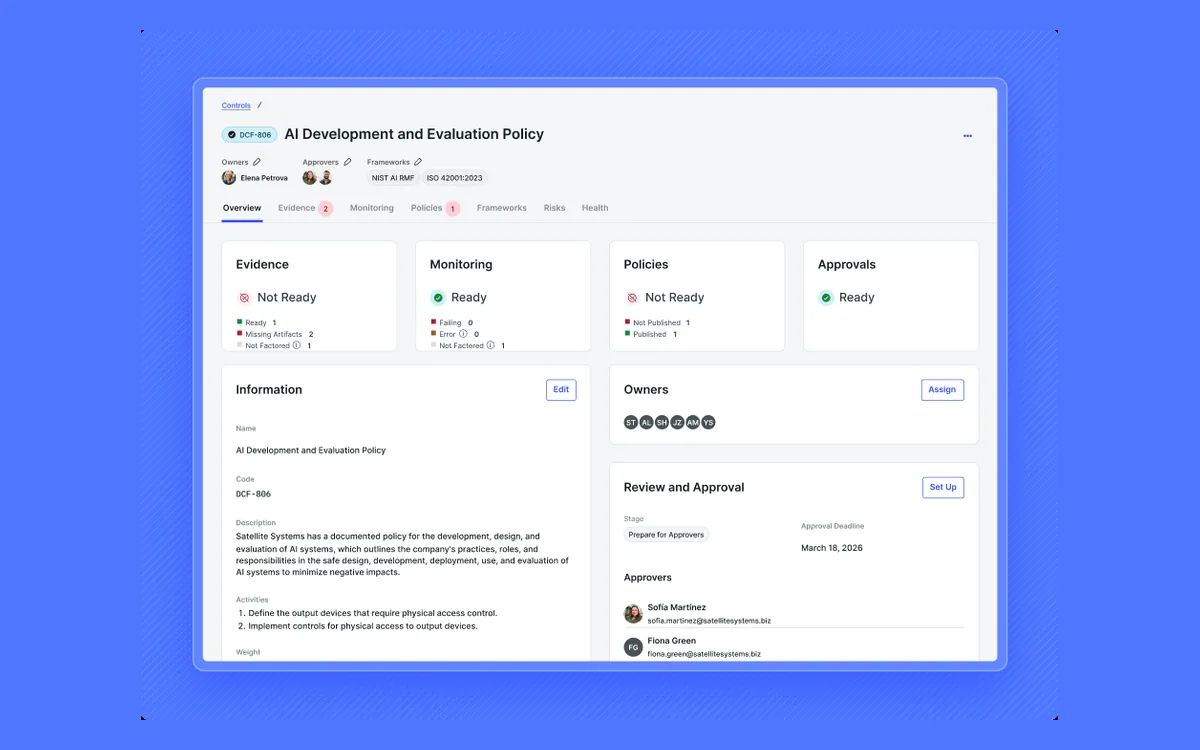
What each product looks like

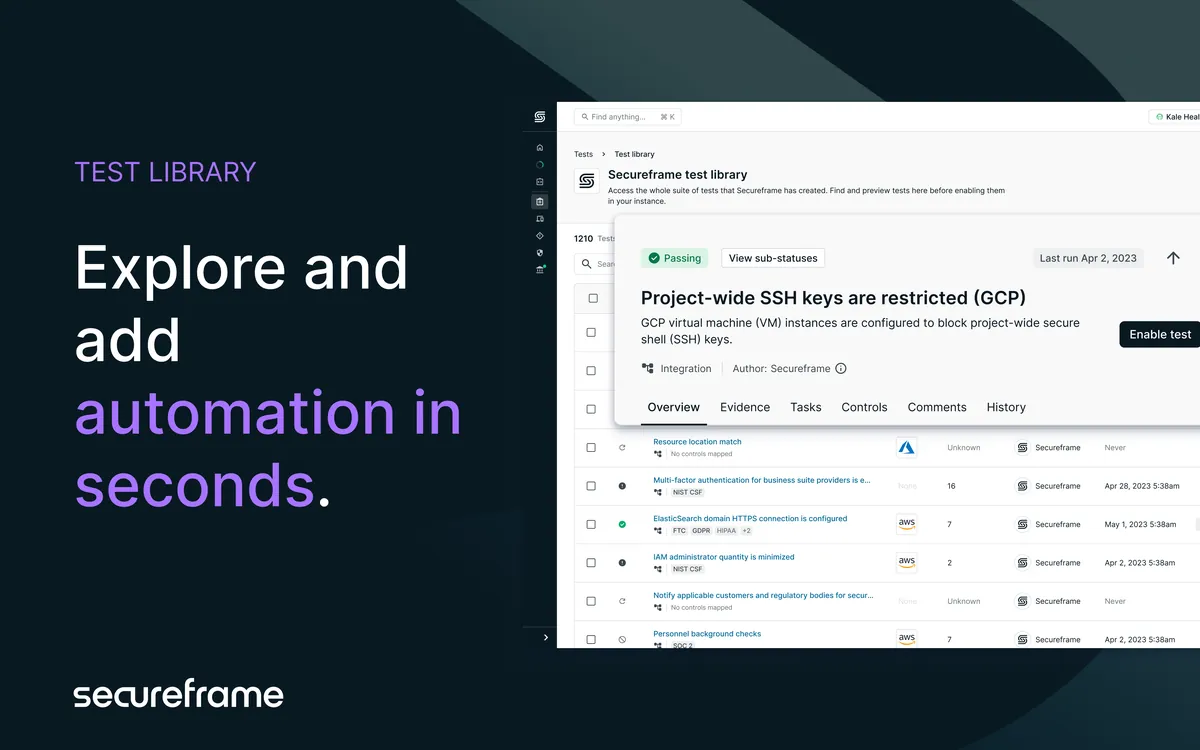
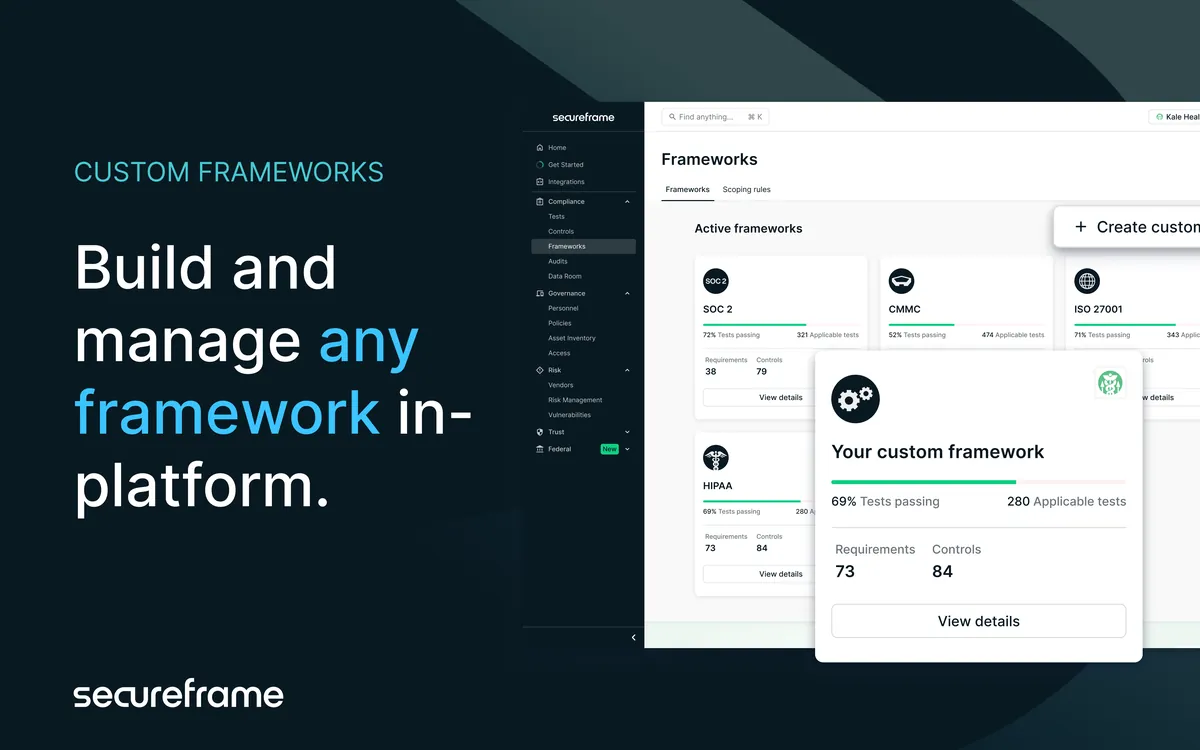
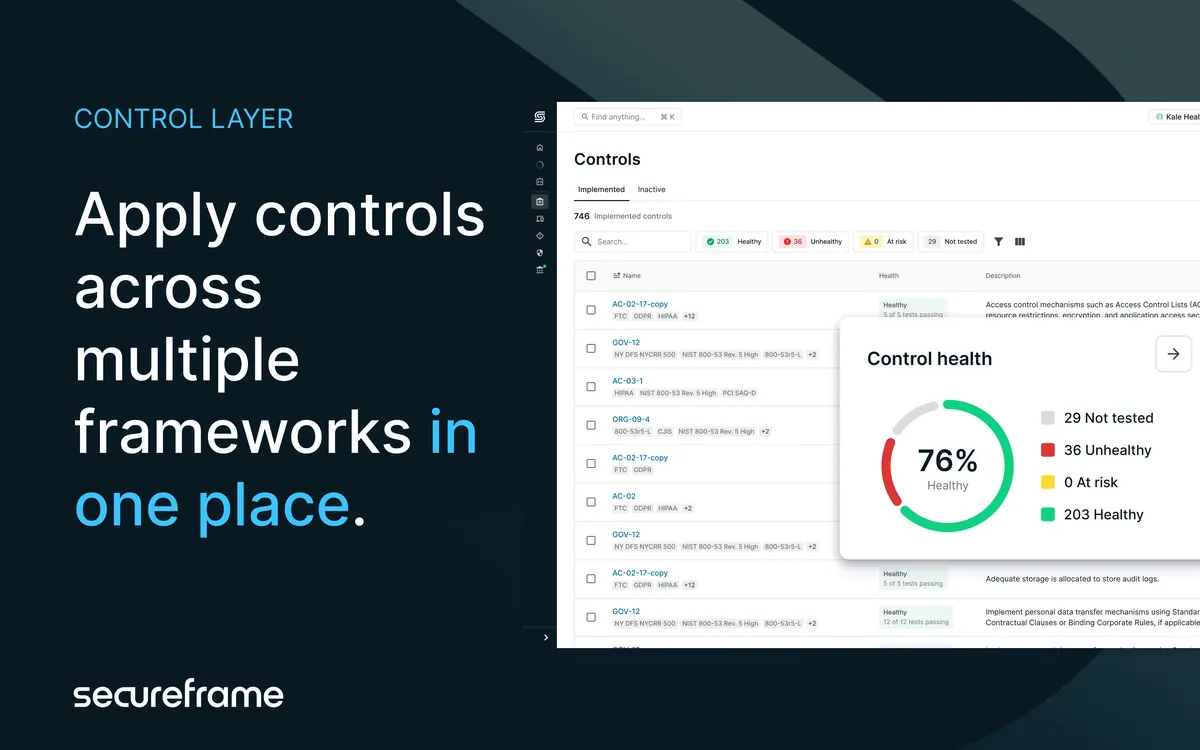
Screenshots published by each vendor on its website or G2 listing, credited below each image.

Strengths and limitations

Drata

Strengths

  • Listed by the most audit firms in SOC2Auditors.org's directory (49). [4]
  • G2 users rate its support 9.5, against Vanta's 8.9. [8]
  • Custom tests with visible raw output, and compliance checks in infrastructure code. [9][10]

Limitations

  • Observed contract median of $25,000 on Vendr, third-highest of the seven platforms with Vendr data, after Hyperproof and Thoropass. [2]
  • Tests run once a day by default, at 7 pm Pacific, not hourly; manual reruns are available. [11]
  • SCIM is listed only on the Enterprise plan; the Foundation plan is capped at 50 employees and one framework. [5]

Secureframe

Strengths

  • Fundamentals package price published on the vendor site: from $7,500 a year. [6]
  • 300+ native integrations. [6]
  • Trust centre included free on Fundamentals. [3]

Limitations

  • SSO and SCIM require the quote-based Complete package. [6][12]
  • Fewer directory auditors than Drata, Sprinto or Vanta (13). [4]

Five tests to run on both before you sign

  1. Connect your three most important systems

    Use a trial or sandbox to connect your cloud provider, identity provider and code host, and check that each produces evidence without manual uploads.

  2. Ask your auditor which one they work in

    An auditor who already works in a platform usually needs less back-and-forth on evidence.

  3. Get both quotes on the same written scope

    Employees, frameworks, modules, support level, contract term, renewal cap, and the audit as its own line.

  4. Check what is an add-on

    SSO, SCIM, extra frameworks, questionnaires and trust-centre features are often tier-gated. Ask for the full price of the scope you need.

  5. Ask how you would leave

    Confirm you can export policies, evidence with timestamps and test history, and whether read-only access continues after the contract ends.

Alternatives and related comparisons

Frequently asked questions

Answers use the figures on this page. Where something isn't disclosed, the answer says so.

Is Drata or Secureframe cheaper?

Secureframe's typical price is lower ($20,000 median against $25,000 median). Prices depend on employees, frameworks and modules, so compare quotes for the same written scope.

Which has more integrations, Drata or Secureframe?

Both publish 300+ integrations. Counts are vendor claims; test the systems you depend on.

Do more auditors work with Drata or Secureframe?

Drata is listed by more audit firms in SOC2Auditors.org's directory (49 vs 13).

Which is rated higher on G2, Drata or Secureframe?

On G2, Drata rates 4.7 from 1,397 reviews and Secureframe 4.7 from 835. Ratings come from self-selected reviewers.

Which is faster to implement?

G2 reviewers report 2 months for Drata and 2 months for Secureframe. Your own timeline depends on scope and how much evidence already exists.

Can Drata or Secureframe include the SOC 2 audit?

Drata doesn't sell the audit; you hire a firm separately. Secureframe doesn't sell the audit; you hire a firm separately.

Can I switch from Drata to Secureframe mid-audit?

You can, but it is risky during a Type 2 observation period, because your auditor needs continuous evidence for the whole period. Most teams switch between observation periods.