
Best for the lowest typical price
Scrut Automation
$7,250 median a year, against Secureframe's $20,000 median.
- Price per year
- $5,160–$27,050Third-party[4]
- G2 rating
- 4.9 · 1,338 reviewsUser reviews[3]
Compliance platform alternatives
Filter by what you need. The table and the profiles below update together.
| Best for | Reason to compare | Frameworks | Profile | |||||
|---|---|---|---|---|---|---|---|---|
| Growth-stage tech teams managing SOC 2 alongside other frameworks | A lower typical price ($7,250 median vs $20,000 median); SCIM provisioning as standard | $5,160[4] to $27,050 |
4.9 (1,338) | 60 listed[25] |
1 directory firm[32] |
Full profile ↓ | ||
| Engineering-led teams that value inspectable code or the option to self-host | A larger integration catalogue (580+ vs 300+); a faster rollout (1 month vs 2 months on G2) | 4.7 (74)Small sample | 580+[15] |
Full profile ↓ | ||||
| Teams preparing a first SOC 2 without an in-house compliance lead | A lower typical price (from $7,500 vs $20,000 median); SCIM provisioning as standard | $7,500[1] "from" price |
4.7 (779) | 80+[2] |
150+[2] |
0 directory firms[8] |
Full profile ↓ | |
| Early- to growth-stage SaaS teams seeking guided first-audit preparation | A lower typical price ($15,000 median vs $20,000 median); more choice of auditor (44 directory firms vs 13) | $13,167[4] to $16,000 |
4.7 (1,685) | 25+ automated[13] |
300+[13] |
44 directory firms[6] |
Full profile ↓ | |
| Teams wanting software and a connected audit process from the same provider | The audit from the same provider; SCIM provisioning as standard | $1,145[4] to $52,209 |
4.7 (586) | 18 named[27] |
200+[31] |
Own CPA firm[5] |
Full profile ↓ | |
| Cloud-native SaaS teams on mainstream stacks that want broad, prebuilt coverage | A larger integration catalogue (400+ vs 300+); more choice of auditor (40 directory firms vs 13) | $7,500[4] to $57,221 |
4.5 (2,853) | 35+[11] |
400+[11] |
40 directory firms[6] |
Full profile ↓ | |
| Growth-stage SaaS teams that expect to add frameworks and want configurable tests | More choice of auditor (49 directory firms vs 13) | $9,415[4] to $68,250 |
4.7 (1,397) | 30+[12] |
300+[16] |
49 directory firms[6] |
Full profile ↓ | |
| Established GRC teams running several frameworks and audits at once | SCIM provisioning as standard | $22,215[4] to $70,000 |
4.5 (223) | 160+[28] |
Full profile ↓ | |||
∅ No alternative matches every filter. Remove one, or . Products with undisclosed data never match a filter that needs it. | ||||||||
● vendor-reported · ○ third-party · ◐ user reviews · ≈ our estimate · ∅ not disclosed. Numbers in brackets link to sources.
How this list is ordered By how many of the reasons above each product meets, using the criterion stated under each reason, then alphabetically. Numbers are list positions, not scores.
The short answer
This page compares Secureframe alternatives on cost, integrations and auditor choice. On our figures, Scrut Automation has the lowest typical price ($7,250 median), Comp AI publishes the largest integration catalogue (580+) and Drata is listed by the most audit firms (49). Thoropass runs the audit through its related CPA firm. Comp AI can be self-hosted. Secureframe still fits teams that want expert guidance on clearly named packages.
Where Secureframe stands today
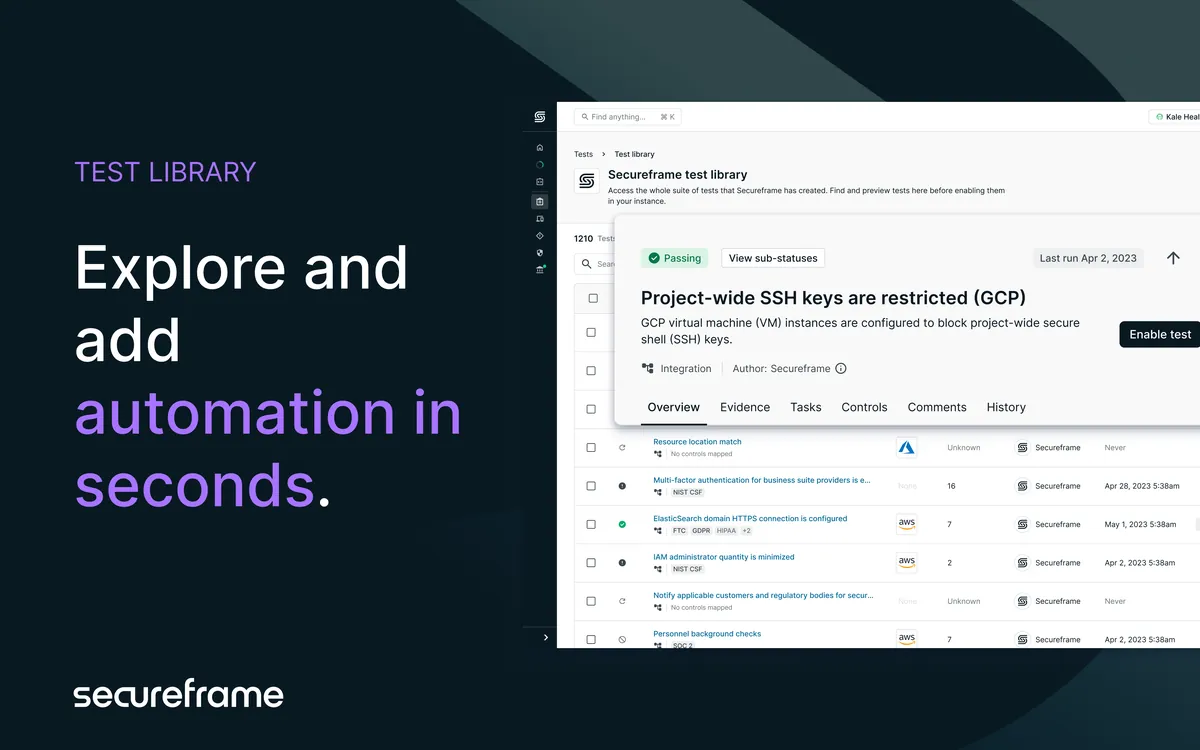
5 common reasons, each tested against the same figures for every alternative. Find yours, then jump to the alternatives that meet it.
Vendr reports observed Secureframe contracts from $7,733 to $32,575 a year, with a median of $20,000 (Vendr; Fundamentals from $7,500).
Counts as addressed when: Has a lower typical price: a Vendr median below $20,000, or a published starting price below it where there is no median.
Secureframe lists 300+ integrations. On G2, "Integration issues" is among its most-mentioned complaints (184 G2 mentions). Systems it doesn't cover need their evidence collected by hand.
Counts as addressed when: Publishes a larger integration catalogue than Secureframe's 300+.
13 attestation firms in SOC2Auditors.org's directory list Secureframe as a platform they work with. A larger pool makes it easier to choose or change auditor without changing tools.
Counts as addressed when: Listed by more firms than Secureframe (13) in the same directory, or the provider runs the audit itself.
SCIM provisioning: add-on or higher tier.
Counts as addressed when: Includes at least one of these as standard: SCIM provisioning.
G2 reviewers put Secureframe's time to implement at 2 months.
Counts as addressed when: Shorter G2 time to implement than Secureframe's 2 months.
Switching mid-programme has real costs. Staying is often the right call if any of these apply.
Before renewing, ask one alternative to quote for exactly your current scope (frameworks, employees, modules and audit), and take that quote into your Secureframe renewal.
Four common situations and the alternative that fits each. These are fit labels, not rankings.
Best for the lowest typical price
$7,250 median a year, against Secureframe's $20,000 median.
Best for integration breadth
580+ integrations by the vendor's own count, the largest published catalogue here.
Best for choice of auditor
49 firms in SOC2Auditors.org's directory list it, the most of any alternative here.
Best with the audit from the same provider
Runs the audit through its related CPA firm, Thoropass Assurance. Software and audit are priced separately.
Each alternative gets the same profile: who it fits, the data, how it differs from Secureframe, and what switching involves.
·
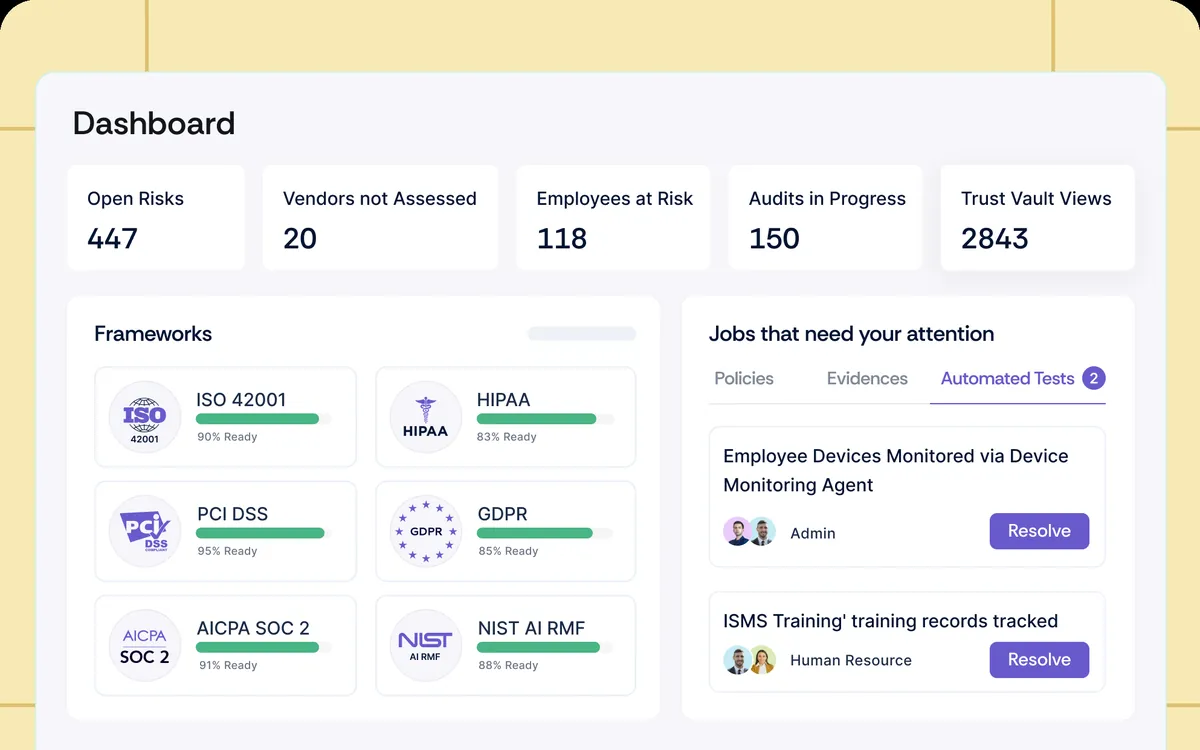
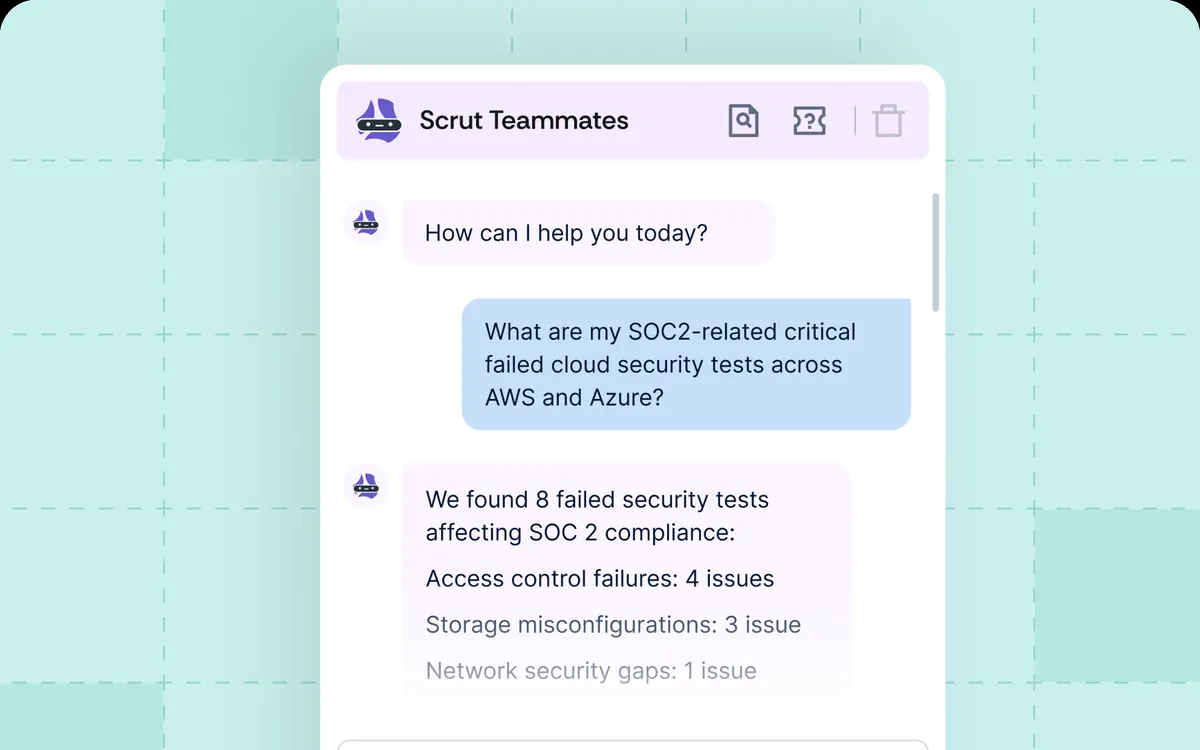
Compliance and risk platform for growth-stage tech teams running SOC 2 alongside other frameworks.
Open-core compliance platform whose evidence-collection code can be inspected or self-hosted, with a managed cloud option.
Compliance automation platform sold in packages that pair the software with consultants, aimed at a first SOC 2.
Compliance automation platform focused on guided first-audit preparation for SaaS teams.
Compliance platform paired with its related CPA firm, Thoropass Assurance, so software and audit come from one provider.
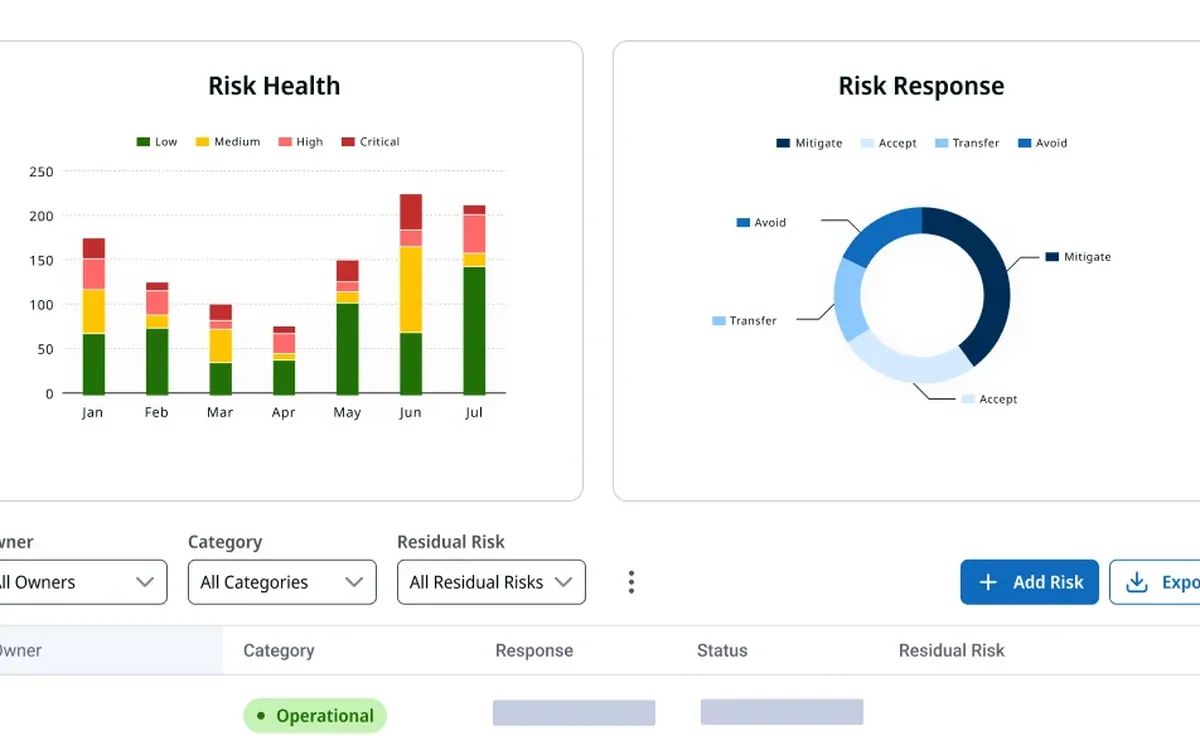
Compliance automation platform with the largest published integration catalogue and hourly automated tests.
Compliance automation platform with custom tests, compliance checks in infrastructure code and a dedicated auditor portal.
Governance, risk and compliance platform for established teams running several frameworks and audits at once.
No profiles match the current filters.
On typical prices (the Vendr median, or the published starting price where there is no median): Scrut Automation $7,250 median, Scytale from $7,500, Sprinto $15,000 median, Vanta $20,000 median, Drata $25,000 median, Thoropass $26,927 median, Hyperproof $41,400 median. Comp AI doesn't publish a price. Secureframe's own typical price is $20,000 median. Medians and starting prices aren't like for like, so compare quotes for the same scope.
Annual platform subscription on one scale, Secureframe first as the baseline. Ranges are observed contracts (Vendr); a fading bar is a published "from" price; the black tick is a median; hatching means no price is published.
Secureframe is the shaded baseline column. Tick the alternatives you're weighing, then compare only those.
| Capability | SecureframeBaseline | Scrut Automation | Comp AI | Scytale | Sprinto | Thoropass | Vanta | Drata | Hyperproof |
|---|---|---|---|---|---|---|---|---|---|
| SOC 2 | Included | Included | Included | Included | Included | Included | Included | Included | Included |
| ISO 27001 | Included | Included | Included | Included | Included | Included | Included | Included | Included |
| HIPAA | Included | Included | Included | Included | Included | Included | Included | Included | Included |
| Auditor workspace | Included | Included | Partial | Included | Included | Included | Included | Included | Included |
| Trust centre | Included | Included | Included | Included | Included | Included | Included | Included | Partial |
| SCIM provisioning | Add-on or higher tier | Included | Not disclosed | Included | Not disclosed | Included | Add-on or higher tier | Add-on or higher tier | Included |
| Audit from the same provider | Not offered | Not offered | Add-on or higher tier | Add-on or higher tier | Not offered | Included | Add-on or higher tier | Not offered | Not offered |
| Self-hosting option | Not disclosed | Not disclosed | Included | Not disclosed | Not disclosed | Not disclosed | Not disclosed | Not disclosed | Not disclosed |
Capability states come from the sources cited in each profile; most are from [5][23][2][20][21][12][22][24][26][28].
These come up in the same searches but solve a different problem. Each is sometimes the better answer.
Publish your security posture and answer questionnaires, but don't monitor controls or collect audit evidence.
Right instead when you already hold a SOC 2 report and buyer security reviews are the bottleneck.
Write policies and run readiness work, usually alongside a platform you still pay for.
Right instead when the problem is time, not software.
Some audit firms include a licence for their own tool with the audit fee.
Right instead when you want one relationship and accept the firm's tool. Check what happens to your data if you change auditor.
Cover risk, policy and audit management across a large organisation, with implementations measured in quarters.
Right instead when you have a dedicated GRC team and many frameworks.
Five steps, in order. Most failed switches skip the first or second.
Download policies, evidence with timestamps, the risk register, vendor reviews and any test history. Some exports are only available while your contract is active.
Switch between observation periods, not during one. If the renewal falls mid-period, ask Secureframe for a short extension rather than moving tools mid-audit.
Confirm they can audit from the new platform or accept its exports.
Connect the new platform and compare its test results with Secureframe's for about 30 days before relying on it.
Your auditor may ask for evidence from the old system. Negotiate read-only access, or keep a dated archive of every export.
Answers use the figures on this page. Where a vendor hasn't disclosed something, the answer says so.
On typical prices (the Vendr median, or the published starting price where there is no median): Scrut Automation $7,250 median, Scytale from $7,500, Sprinto $15,000 median, Vanta $20,000 median, Drata $25,000 median, Thoropass $26,927 median, Hyperproof $41,400 median. Comp AI doesn't publish a price. Secureframe's own typical price is $20,000 median. Medians and starting prices aren't like for like, so compare quotes for the same scope.
By vendor claims: Comp AI 580+, Vanta 400+, Drata 300+, Sprinto 300+, Thoropass 200+, Scytale 150+. Scrut Automation and Hyperproof don't publish a count. Secureframe publishes 300+. Counts are not proof that your own systems produce evidence your auditor accepts, so test the integrations you depend on.
In SOC2Auditors.org's directory: 49 firms list Drata, 44 firms list Sprinto, 40 firms list Vanta, 1 firm lists Scrut Automation, 0 firms list Scytale. Thoropass runs audits through its related CPA firm. Hyperproof and Comp AI aren't counted. Secureframe: 13 firms.
Thoropass pairs its platform with a related CPA firm, Thoropass Assurance, though software and audit are priced separately. Vanta sells a package that can include an independent auditor's fee. Comp AI says audits can be included in its quote. Scytale sells a third-party audit service from $4,200. The others sell the platform only; you hire an audit firm separately.
Not among full managed platforms. Comp AI publishes an AGPLv3 open-core codebase you can self-host, which removes the licence fee but moves operations onto your team; its managed service is quoted on a call.
On G2: Scrut Automation 4.9 (1,338 reviews), Sprinto 4.7 (1,685 reviews), Drata 4.7 (1,397 reviews), Scytale 4.7 (779 reviews), Thoropass 4.7 (586 reviews), Comp AI 4.7 (74 reviews), Vanta 4.5 (2,853 reviews), Hyperproof 4.5 (223 reviews). Secureframe is rated 4.7 from 835 reviews. Ratings come from self-selected reviewers, and small review counts move more easily.
You can, but it is risky during a Type 2 observation period, because your auditor needs continuous evidence for the whole period. Most teams switch between observation periods, or agree in writing with their auditor how evidence from both tools will be accepted.